TCPA consent you can connect to the actual lead
A field marked consented does not explain what a consumer agreed to. ConsentVerified captures the disclosure and submission action, issues a certificate, and helps your team verify the evidence before outreach. Review the seller, number, channel, and context together so an intake decision rests on the recorded interaction rather than a lead source's broad promise.
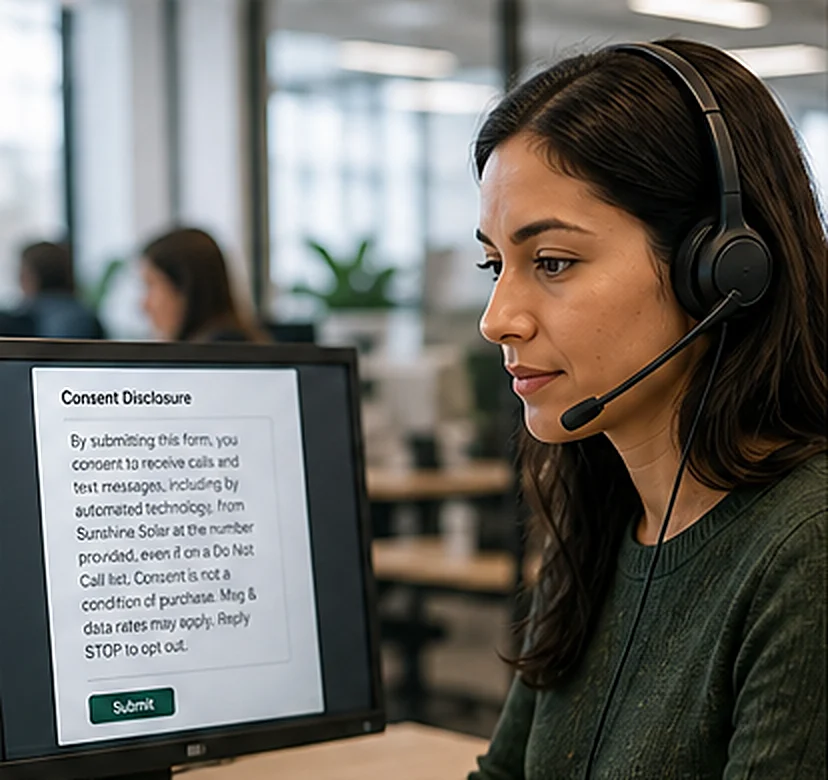
Understand when written consent matters
The TCPA and FCC rules require prior express written consent for certain telemarketing calls and texts, including covered marketing calls using an automatic telephone dialing system or an artificial or prerecorded voice. Requirements depend on the technology, destination, purpose, and applicable exemptions. A manual outreach method does not automatically remove other federal or state obligations, including do-not-call rules.
For covered telemarketing, the written agreement must clearly authorize the seller to deliver or cause delivery of the relevant calls or messages to the specified number using the covered technology. It must include a clear disclosure that consent is not a condition of purchasing property, goods, or services. An electronic signature can qualify when it satisfies applicable electronic signature requirements. Preserve the action and wording together so counsel can assess the record.
- Identify the communication and technology the consumer authorizes.
- Connect the agreement to the telephone number provided.
- Keep the affirmative action that supports the electronic agreement.
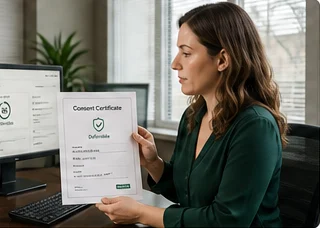
Check the elements behind the agreement
Review the full form experience, including the placement and readability of the disclosure. Required language that consumers cannot reasonably see can create problems even when the text exists in the page source. The Consent Language Checker identifies wording gaps and explains its checks so your team can revise the form before relying on it to collect permission.
The checklist supports review of seller identification, the selected communication channels, relevant technology wording, the purchase condition disclosure, and the action used to signify agreement. Your team should also check the relationship between the disclosure, the number field, and the submission control. For messaging-specific details, review SMS consent form elements alongside the TCPA analysis.
- The seller receiving authorization is identifiable from the disclosure.
- The phone number and authorized channels are connected to the agreement.
- Covered technology and artificial or prerecorded voice wording match the outreach.
- The disclosure explains that consent is not a condition of purchase.
- The agreement uses a clear affirmative action supported by an appropriate signature process.
Preserve the form the consumer actually encounters
ConsentVerified captures the disclosure text, its visibility, checkbox or button action, timestamps, page URL, IP address, and user agent. It links the record to a certificate ID and SHA-256 hash. That gives your team evidence of the captured interaction rather than a screenshot of a form that might have changed since the lead was collected.
The proof of consent workflow connects that capture to verification and retention. Keep the certificate ID with the lead throughout intake and handoff. A certificate records the event the system captures, but it does not prove the submitter's identity or decide every question about enforceability. Review the evidence in context, especially if the number, seller, or intended use differs from what the record shows.
-
Preserve the disclosure associated with the submission rather than the latest form version.
-
Keep the certificate reference connected to the relevant lead record.
-
Review the captured action and context before relying on the agreement.
Review seller authorization when leads change hands
Buying a lead does not by itself establish that the consumer authorizes your business to contact them. Review the disclosure and the sellers it identifies, the communication contemplated, and the proposed use of the lead. Broad references to partners can leave uncertainty about the consumer's agreement. ConsentVerified checks the seller named in the record so buyers can investigate a mismatch before outreach.
The FCC one-to-one consent rule was vacated by the Eleventh Circuit in January 2025 and never took effect. Do not describe that vacated rule as a current requirement. Existing TCPA consent obligations and other applicable federal and state rules still matter. Seller-specific review remains a useful way to assess evidence without claiming that the vacated rule mandates a separate agreement for every transaction.
- Request the underlying consent record from the lead source.
- Compare the disclosure with your identity and intended outreach.
- Resolve unclear authorization before sending the lead into an outbound workflow.
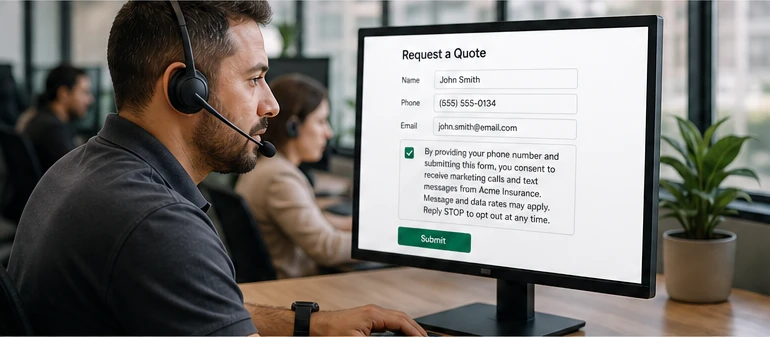
Give intake teams a consistent review process
Use the Lead Verification API to check the phone match, named seller, age of consent, and disclosure score. Define the records your team accepts and route missing or failed checks for review. A disclosure score helps prioritize issues, while the captured agreement provides the facts needed to decide whether the proposed outreach fits the permission obtained.
Consent age is an operational signal rather than a universal legal expiration date. A recent record can still be inadequate, and an older agreement requires context rather than an invented cutoff. Combine these checks with DNC list scrubbing and current suppression information. A certificate check alone does not establish that a number is callable under every rule that applies.
- Confirm the phone number matches the certificate you receive.
- Check whether the intended seller is named in the captured disclosure.
- Investigate incomplete evidence before routing a lead for contact.
Keep later requests connected to contact decisions
Consent records describe permission at a point in time. A consumer can later revoke consent through reasonable means under applicable rules. Your process needs to recognize and honor relevant requests, including requests received outside the original form. Do not rely only on the initial certificate when a later conversation, message, or support interaction changes the person's contact preference.
Keep internal suppression lists connected to intake and outbound operations. Preserve the request and the handling evidence, including STOP interactions for messaging, so reviewers can understand what happens after opt-in. Your staff should have a clear process for escalating ambiguous requests and applying the relevant scope and timing rules. ConsentVerified is a compliance tool, not a law firm. This information is not legal advice.
-
Record requests to stop and route them to the responsible team.
-
Check internal suppression before releasing a record for outreach.
-
Retain the original agreement and later revocation evidence for review.
Put retained evidence behind your compliance process
TCPA statutory damages can range from $500 to $1,500 per violating call or text, with the higher amount depending on a court finding a knowing or willful violation. Evidence does not eliminate exposure or guarantee a defense, but it gives your team a record to examine when a complaint or counsel request arrives. The Evidence Vault exports PDF and JSON packages per phone number.
Plans start from $149 a month with Starter. Growth, Scale, and Enterprise support larger workflows and different retention needs. Compare TCPA compliance software pricing and consent data security to choose capacity, storage, and access controls appropriate for your team. The one-off home page checker lets you review disclosure wording before choosing a subscription.
Start with the disclosure your leads see
Check the wording, capture the interaction, and verify the record before making a contact decision. Create your workspace to connect these steps and keep the evidence available when your compliance team needs to examine the agreement behind a lead.